Cloud architecture and operational resilience
Align platform investment with service availability, operating cost and recovery priorities.
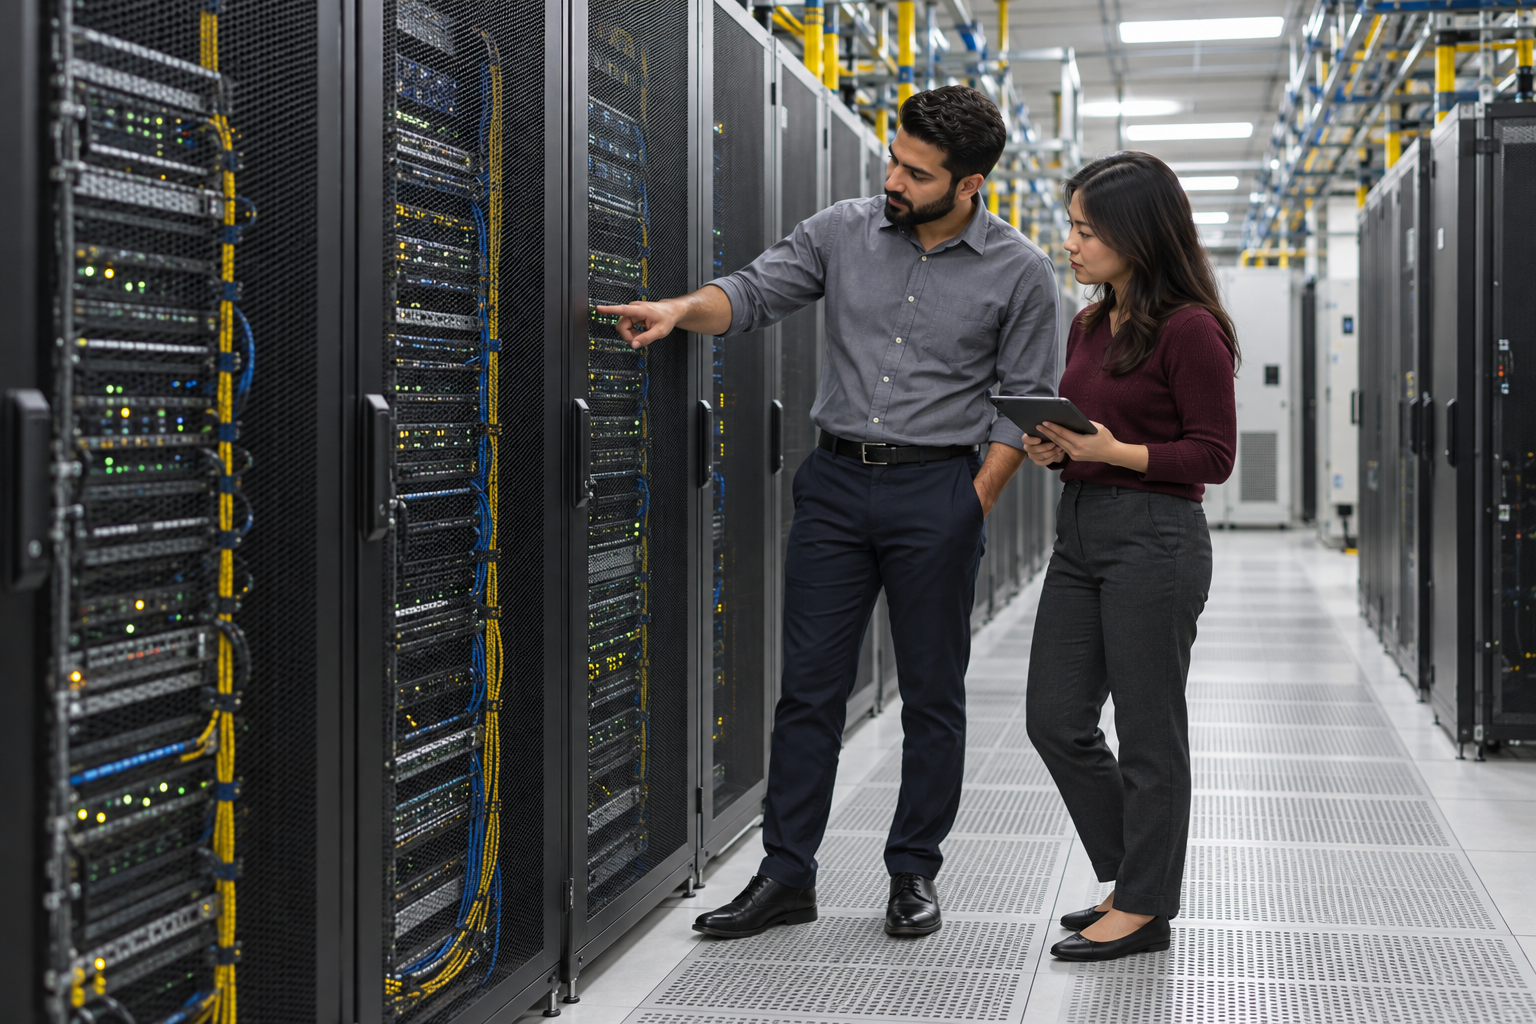
Design deployment and operation around workload behavior, business obligations and recovery requirements. Evaluate public, private and hybrid environments against measured capacity and explicit responsibilities.
Cloud, virtualized and clustered systems
Design the deployment around workload behavior, availability targets, data location, performance and cost. Assess virtualization, clustering, service isolation, capacity and recovery requirements as connected decisions.
A move to cloud services changes operating responsibilities; it does not remove the need for backup, recovery testing, access control or cost management. Capacity and resilience should be demonstrated with measured workloads and failure scenarios.
Capacity planning considers normal demand, peak activity, concurrency, information growth and the effect of a dependency becoming slow or unavailable. Compute, memory, storage and network behavior must be evaluated together. Additional instances do not solve a bottleneck in a shared database, a constrained external service or an inefficient application workflow.
Availability design defines failure boundaries and the behavior expected when a component is lost. Clustering, load distribution, session handling and shared state must support that design. Recovery objectives also determine backup arrangements, replication choices and the sequence in which dependent services are restored.
Virtualization and service isolation can improve deployment flexibility, but their resource and administrative requirements still need to be understood. We assess configuration, observability and the practical ability of the operating team to diagnose and recover the environment. Qualification should include representative load and controlled failure exercises, with the results reflected in operating guidance.
Public, private and hybrid cloud
Select an environment against the workload and its obligations. Public cloud provides shared service platforms with several tenancy and management options. Private environments provide dedicated organizational control. Hybrid designs connect environments where business or technical requirements justify it.
Security and compliance depend on the chosen services, contracts, configuration, data handling and implemented controls. Define provider and customer responsibilities explicitly; the public or private label alone does not establish compliance.
Compare provisioning, hardware and performance options, service limits, support scope, pricing commitments and exit requirements before deciding. Managed and self-managed arrangements have different operating responsibilities.
Public-cloud assessment includes the services being consumed, the available isolation options, the location of information and the responsibilities retained by the customer. Access management, service configuration, application behavior and data handling remain important even when underlying infrastructure is operated by a provider. The assessment must follow the actual service model.
Private environments can provide control over architecture, placement and operating practices, while also placing responsibility for capacity, maintenance and recovery on the organization or its service partner. Dedicated infrastructure is not a substitute for effective access control, secure configuration, tested recovery or continuing maintenance.
Hybrid architecture requires deliberate treatment of the connections between environments. Identity, network boundaries, information movement, monitoring and recovery procedures must remain coherent across them. Latency, data-transfer cost and dependency availability can materially affect where a workload should run.
An architecture assessment compares these options against business requirements and operating capability. The decision records trade-offs, assumptions and responsibility boundaries, with a plan for migration and eventual exit or replacement. Cost analysis should include support, connectivity, data transfer, resilience and the continuing effort needed to run the system.
Delivery and operational resilience
Make builds reproducible, qualify changes in staging and retain a clear promotion and rollback path. Define monitoring, diagnostic evidence, dependency maintenance and recovery procedures with the team that will operate the system.
Document service ownership, capacity assumptions, backup and restore procedures, and the boundaries of any support engagement. These are part of the engineering deliverable.
A repeatable build should identify its source, dependencies and configuration requirements. Development environments and delivery instructions need to be usable by the people who will maintain the application. Configuration and credentials are managed separately from application source, while interface and deployment documentation explain the dependencies required for operation.
Staging qualification tests the changes that will be released, including their effects on existing workflows and integrations. Promotion requires retained backups, explicit verification and a recovery path appropriate to the change. Database and interface compatibility need particular attention when components are released on different schedules.
Operational readiness includes monitoring that supports diagnosis, a maintained inventory of dependencies, documented restore procedures and clear escalation ownership. Recovery should be exercised rather than inferred from the presence of a backup file. Maintenance planning covers vulnerabilities, compatibility changes, capacity and the eventual retirement of unsupported components.
Support and managed-operation arrangements define coverage, response responsibilities, maintenance activity and reporting. These commitments are agreed around the system being delivered and the operational capacity required to sustain it.
Security and governance throughout delivery
Threat modeling, least privilege, privacy requirements and auditable change control inform the architecture from the start. Continue with verification, vulnerability response and maintenance as the system evolves.
For organizations in financial services, healthcare, commerce and other complex environments, connect technical controls to the relevant business processes, data responsibilities and assurance evidence.
Security architecture identifies the information and operations that require protection, the identities that may access them and the boundaries between components. Implementation work then connects those requirements to authorization, service isolation, data handling and operational controls. Tests need to examine business behavior as well as configuration.
Governance makes these controls accountable. Define the owners of systems and information, the authority to approve changes and the process for handling exceptions. Retain evidence that a control is implemented and operating, including the results of relevant verification and recovery exercises.
Privacy requirements also influence architecture and integration. Information collection, sharing, retention and deletion should be traceable across the services involved. Changes to suppliers, integrations or AI-enabled processing are reviewed against those responsibilities as part of continued operation.