Application security and identity
Protect customer information and consequential business transactions as people, partners and services gain access.
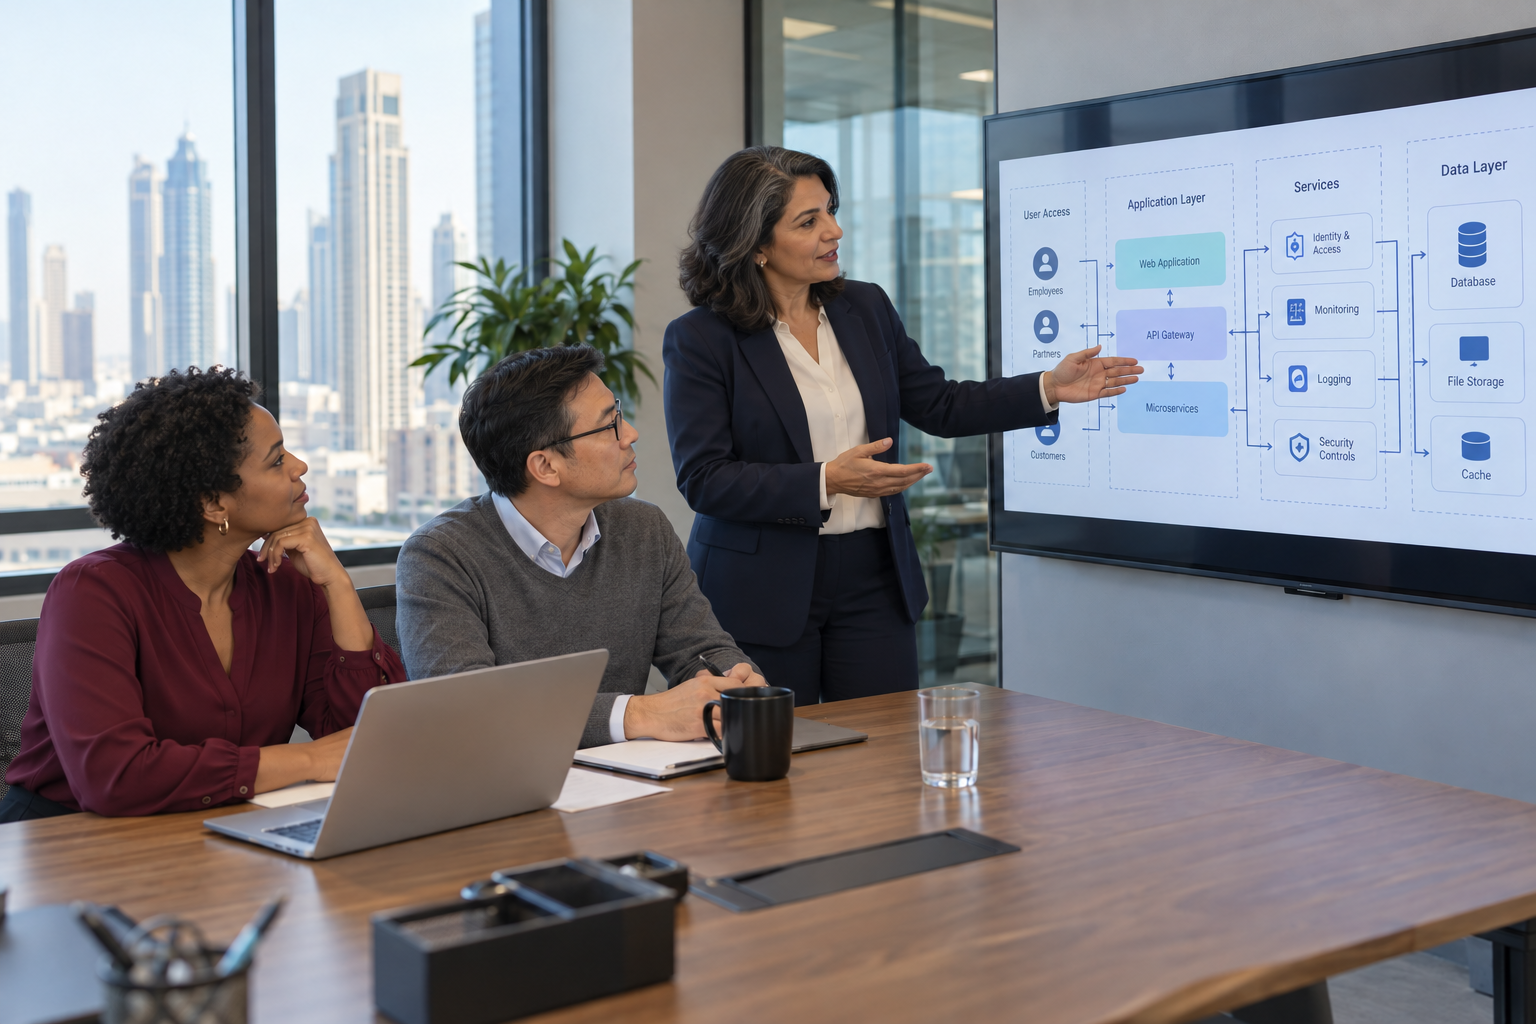
Protect business workflows and the identities authorized to use them. Connect secure application design, access control and account lifecycle management with engineering verification.
Application security from design to operation
Define trust boundaries, protect sensitive workflows and make security requirements part of delivery. Our work covers architecture review, threat modeling, authentication, authorization, data protection and abuse resistance across applications and their integrations.
Turn findings into prioritized engineering work, with verification criteria, controlled releases and a clear path to recovery. Vulnerability management and patching remain part of the lifecycle as software, dependencies and threats change.
We start with the actions that carry business consequences: accessing another customer's information, changing account ownership, approving a payment, publishing content or granting a privilege. Threat modeling examines who can initiate each action, what evidence the system trusts and where that trust can fail. This makes business logic and access control part of the assessment alongside conventional vulnerability checks.
Implementation work can address session handling, input and output validation, service authorization, secrets management, dependency exposure and data protection. Public interfaces also need protection against automated misuse and content that violates the purpose of a workflow. Controls must preserve legitimate activity and provide a defined path for correction, review or recovery.
The deliverable connects findings to affected workflows, engineering changes and repeatable verification. Teams receive a prioritized remediation plan and acceptance criteria that can be retained with the application, rather than a report disconnected from the development backlog.
Identity and access management
Give employees, customers, partners and services the access their roles require. Connect identity sources, authentication and authorization with account provisioning, access reviews and timely removal of privileges.
We address account recovery, privileged access, service identities and auditable approval workflows alongside single sign-on and self-service account management. Delivery can support an internal team, a co-managed service or an agreed outsourced scope.
Identity architecture begins with authoritative records and a clear account lifecycle. Joining an organization, changing responsibilities and leaving it should produce deliberate changes to access across connected systems. Provisioning and deprovisioning workflows need ownership, approval rules, exception handling and reconciliation so that unused accounts and accumulated privileges do not remain unnoticed.
Authentication and authorization are separate design problems. Strong authentication establishes who is present; the application still has to decide which records, transactions and administrative functions that identity may use. We examine role design, delegated administration, privileged operations, multifactor authentication, federation and the recovery procedures that could otherwise become an alternative route to sensitive access.
Service accounts and automated workloads require the same discipline. Their permissions, credential handling, rotation responsibilities and termination conditions should be documented. Typical outputs include an identity integration design, access-control model, lifecycle workflows and a review process that can be operated by your own team.